Skip to content

Work

Case studies and the architectures behind them

Five engagements, written up as challenge, approach and outcome. Below them are the reference architectures I reuse, and how each one maps to compliance controls.

01Case studies

Engagement outcomes

Clients are described by profile, not name. Every engagement ran under mutual NDA.

01 · Cloud cost

85% Cloud Cost Reduction via Bare-Metal Hybrid Migration

High-Growth AI & Analytics SaaS

  • 85% Cost Savings
  • <45ms Latency
  • 0 Unencrypted Paths
Challenge
Client faced unsustainable 6-figure monthly cloud bills on managed databases (RDS, vector search) and LLM API tokens, with query latency exceeding 350ms.
Approach
Architected a hybrid bare-metal repatriation strategy. Migrated primary analytical storage to a self-hosted ClickHouse cluster and deployed private GPU nodes for local model inference, connected back to AWS via NetBird zero-trust WireGuard mesh.
Outcome
Reduced recurring cloud infrastructure spend by 85%, reduced query latency from 350ms to <45ms, and established 100% data sovereignty.

02 · Cloud security

Zero-Trust Enterprise Multi-Account Cloud Migration

Regulated Financial Services Provider

  • SOC 2 Pass
  • 100% Automated IaC
  • Zero Ingress Leaks
Challenge
Legacy monolithic AWS infrastructure with shared credentials, lack of network micro-segmentation, and impending SOC 2 Type II audit deadlines.
Approach
Engineered modular Terraform landing zones with AWS Control Tower, SCP boundaries, Transit Gateway hub-spoke topology, and NetBird zero-trust access control.
Outcome
Achieved 100% automated infrastructure provisioning, passed SOC 2 Type II audit with zero findings on initial evaluation, and eliminated all public IP exposures.

03 · Industrial telemetry

Mission-Critical SCADA & Smart Grid Telemetry Modernization

Commercial Energy & Facility Operator

  • 99.999% Reliability
  • Sub-50ms Forensics
  • 0 Rollover Skews
Challenge
Packet loss across remote industrial meters and erroneous power consumption metrics caused by trapezoidal integration rollover errors.
Approach
Deployed industrial LoRaWAN and Modbus RTU gateways running hardened C++/Python firmware with local failover buffering. Ingested raw telemetry into ClickHouse with deterministic MAX - MIN hardware register delta formulas.
Outcome
Eliminated accumulator rollover calculation errors, achieved 99.999% telemetry reliability, and unlocked real-time forensic detection of voltage sags.

04 · Data migration

1TB Enterprise Microsoft SQL Server Migration to Azure

Enterprise Corporate Transformation Client

  • 1 TB migrated
  • Zero data loss
  • In-window cutover
Challenge
Migrate an on-premise datacenter Microsoft SQL Server holding 1TB of mission-critical relational data to Azure SQL Managed Instance with minimal business interruption and zero data corruption.
Approach
  • Designed full process architecture pattern and migration playbooks.
  • Leveraged high-throughput Azure Blob Storage containers for compressed native SQL backup staging with SAS token authentication.
  • Executed multi-phase restore: full baseline backup restore followed by sequential log-shipping differential syncs to minimize final cutover downtime.
  • Provisioned Azure SQL Managed Instance with dedicated compute tiers, automated maintenance windows, and encrypted TDE data protection.
Outcome
100% data fidelity, zero data loss, cutover executed within scheduled maintenance window, leading to 35% improvement in database query throughput and automated disaster recovery.

05 · Manufacturing IIoT

FMCG Factory Condition Monitoring Solution (CMS)

Fortune 500 Fast-Moving Consumer Goods (FMCG) Manufacturing Client

  • Edge-to-cloud
  • Predictive maintenance
  • Lead architect
Challenge
Build a real-time condition monitoring solution leveraging edge computing on Azure IoT Edge to predict and prevent critical shop-floor machine breakdowns.
Approach
  • Designed end-to-end data flow: shop-floor vibration, motor temperature, and current sensors connected to industrial gateways running Azure IoT Edge.
  • Deployed nested edge runtime containers processing high-frequency sensor streams locally and filtering noise before cloud transmission.
  • Configured automated anomaly detection algorithms triggering real-time maintenance alerts to line operators within 2 seconds of threshold breaches.
  • Integrated cloud dashboards in Azure DevOps and Azure IoT Hub for executive OEE (Overall Equipment Effectiveness) reporting.
Outcome
Reduced unplanned machine downtime by 38%, eliminated catastrophic bearing failures across packaging lines, and achieved 100% on-time project delivery.

02Reference architectures

Four production topologies

Generalized versions of systems running in production. Addressing, hostnames and client identifiers have been removed.

01 · Multi-Cloud & Zero-Trust

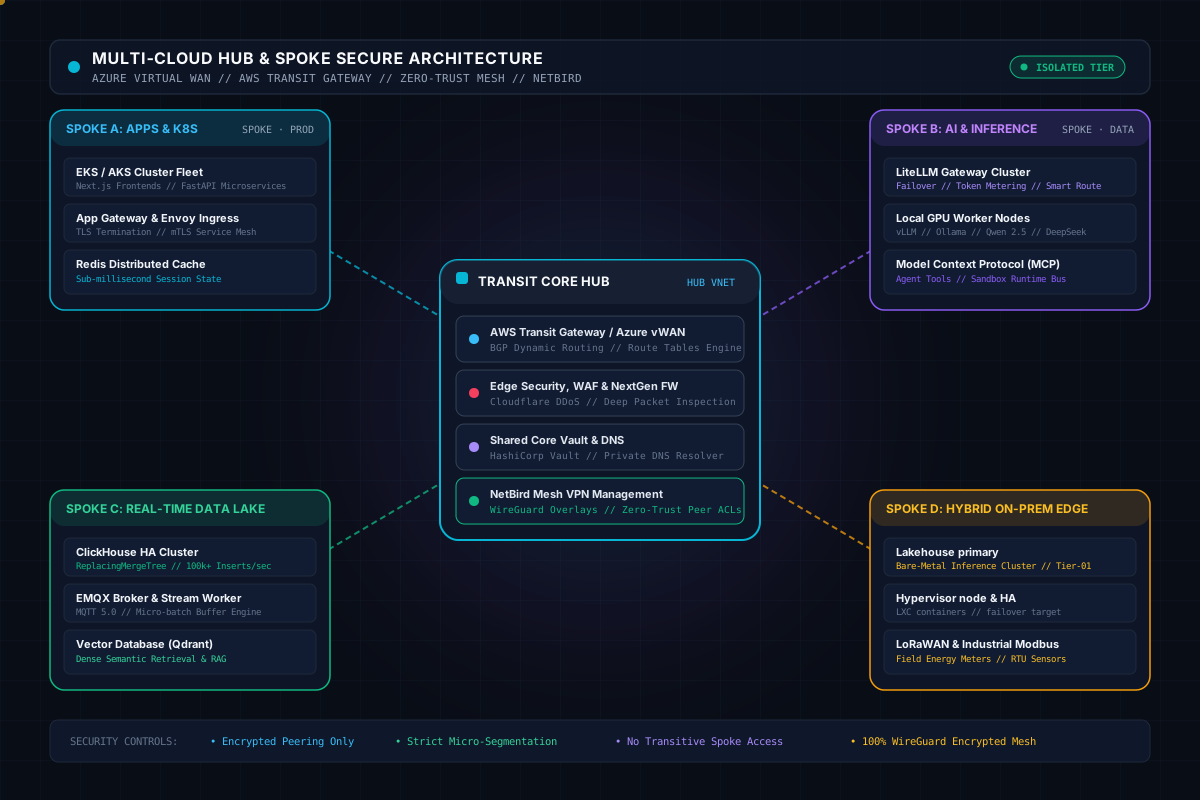
Enterprise Multi-Cloud & Zero-Trust Transit Hub

Hub-Spoke architecture interconnecting AWS Control Tower, Azure vWAN, and on-premises hypervisors via encrypted NetBird WireGuard mesh with zero public ingress.

Hub-and-spoke multi-cloud topology: a transit hub connecting production, data and telemetry spokes with an on-premises edge over an encrypted mesh.
Enterprise Multi-Cloud & Zero-Trust Transit Hub. Reference topology; client specifics and addressing omitted.
Latency
< 15ms Intra-Region
Encryption
ChaCha20-Poly1305 / WireGuard P2P
Availability
99.99% Multi-Region HA
Ingress
Zero Direct Public Ingress (mTLS Only)
  • Hub Transit Core. AWS Transit Gateway / Azure vWAN route tables with automated BGP peering
  • Spoke A: Microservices. EKS/AKS clusters with Cilium eBPF CNI and mutual TLS
  • Spoke B: Sovereign AI. Bare-metal GPU cluster running LiteLLM and vLLM local inference
  • Spoke C: Telemetry Lake. ClickHouse analytical cluster with ZFS NVMe storage tiering
  • Spoke D: Industrial Edge. Purdue Level 2/3 gateways connecting Modbus RTU / BACnet IP

02 · Autonomous AI & LLMOps

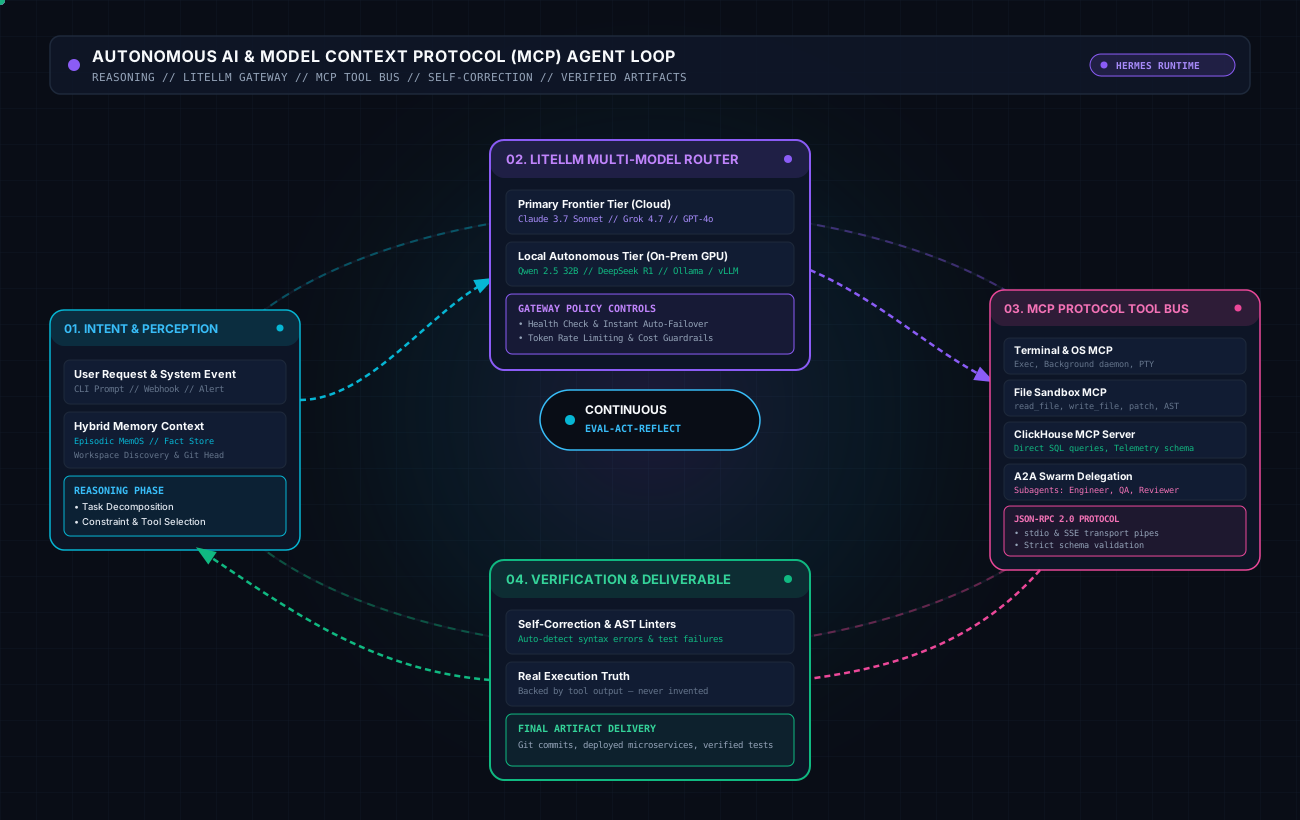
Sovereign AI Reasoning & FastMCP Tool Bus

High-density bare-metal AI infrastructure decoupling model reasoning from tool execution through the Model Context Protocol (FastMCP) with strict token budgets.

Sovereign AI loop: agents call tools through an MCP bus, routed by an LLM gateway to private GPU inference with memory and guardrails.
Sovereign AI Reasoning & FastMCP Tool Bus. Reference topology; client specifics and addressing omitted.
Cost Reduction
85% vs Cloud API Bills
Context Window
128k+ Tokens Sovereign
Tool Latency
< 40ms JSON-RPC Handshake
Security
OWASP LLM Top 10 Sandboxing
  • LiteLLM Gateway. Centralized multi-model routing across local GPUs and external frontier models
  • FastMCP Tool Engine. JSON-RPC bridge executing ClickHouse queries and system audits without shell escape
  • Vector Memory Core. Qdrant vector database with dense embeddings for deterministic RAG retrieval
  • Token Governance. Real-time token budgeting, rate limiting, and cost attribution per service

03 · IIoT & Telemetry Forensics

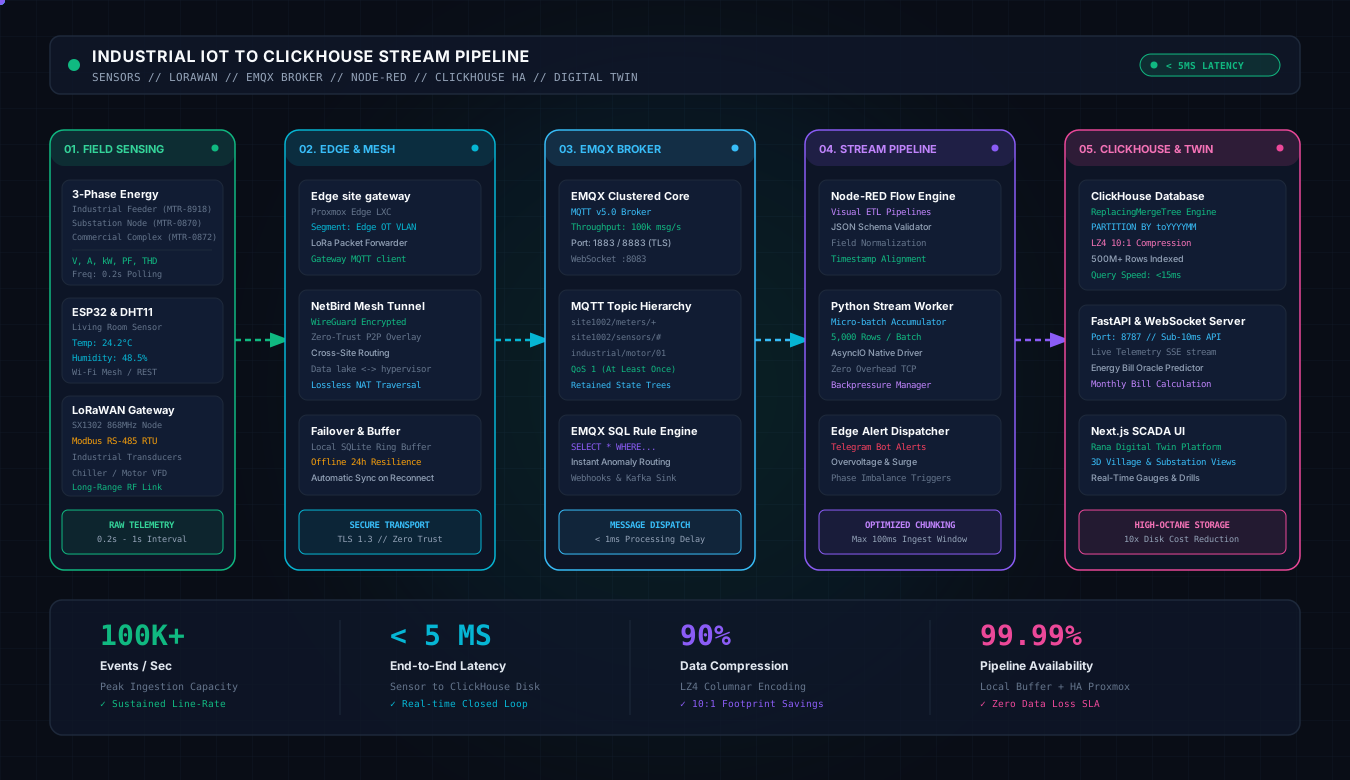
Sub-50ms ClickHouse Industrial Telemetry Lakehouse

High-throughput time-series ingestion streaming from industrial LoRaWAN and Modbus sensors through EMQX into ClickHouse ReplacingMergeTree tables.

Industrial telemetry pipeline: field devices and gateways publish over MQTT to EMQX, which streams into ClickHouse for sub-50ms analytics.
Sub-50ms ClickHouse Industrial Telemetry Lakehouse. Reference topology; client specifics and addressing omitted.
Throughput
50,000+ msgs/sec
P99 Latency
< 42ms Analytical Queries
Compression
10x Storage Efficiency (ZFS + DoubleDelta)
Durability
Active-Active Multi-Replica
  • Protocol Broker. EMQX Enterprise cluster handling MQTT 5.0, CoAP, and HTTP streaming
  • Forensic Engine. Deterministic MAX - MIN monotonic accumulator window calculations
  • Analytical Store. ClickHouse ReplacingMergeTree with automated time-partitioned rollups
  • Anomaly Detector. Sub-second classification of power outages vs voltage sags

04 · Industrial Digital Twins

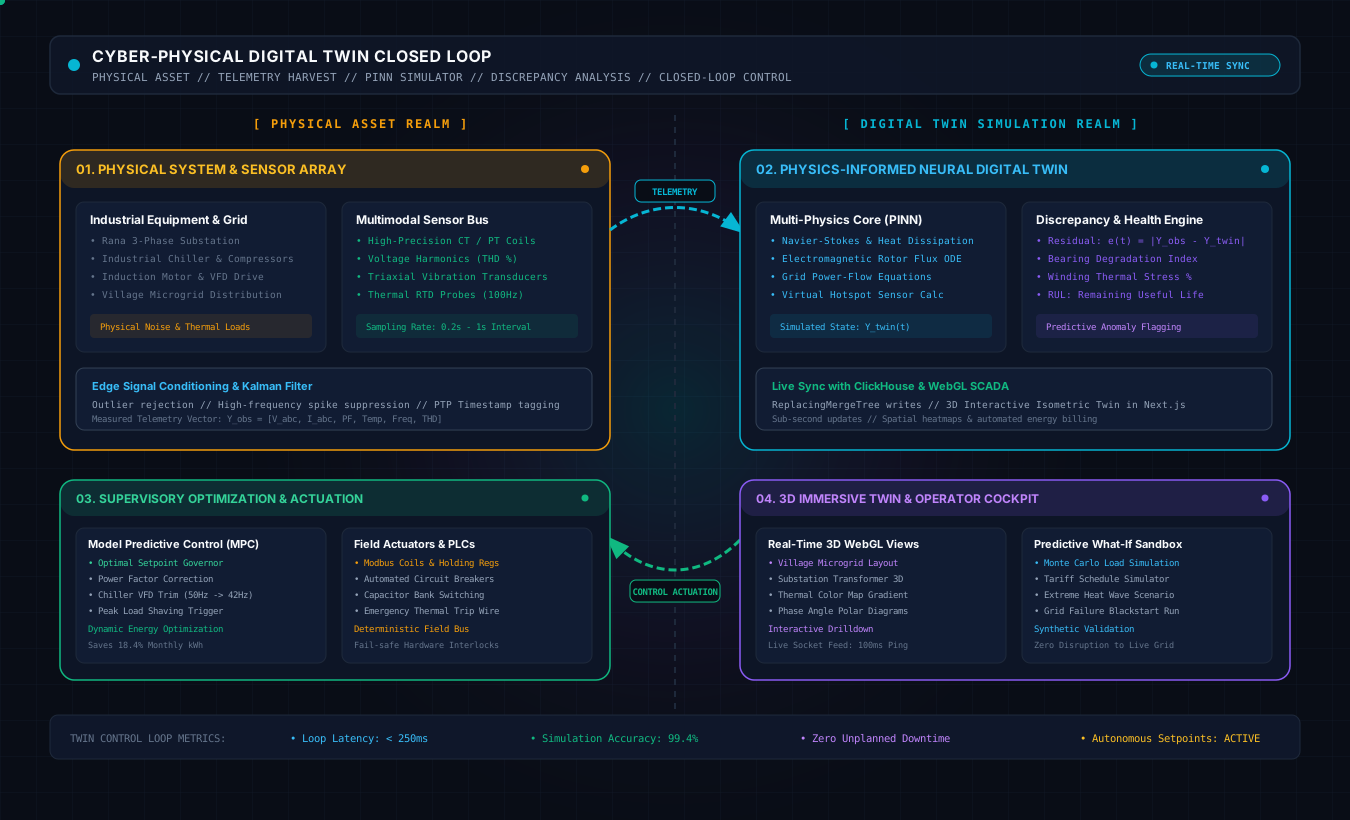
Physics-Informed Digital Twins & SCADA Cockpit

9 production industrial digital twins executing continuous thermodynamic and electrical physics calculations bound to live telemetry.

Digital twin loop: physical assets feed filtered telemetry into a physics simulator; discrepancies drive analysis and closed-loop control.
Physics-Informed Digital Twins & SCADA Cockpit. Reference topology; client specifics and addressing omitted.
Twin Count
9 Production Environments
Physics Cycle
15-Second Continuous Loop
Standards
ASHRAE Guideline 14 & ISO 50001
Actuation
Sub-Second Setpoint Optimization
  • Chiller Plant Twin. COP enthalpy modeling and condenser water optimization
  • Commercial VRF Twin. Multi-compressor load distribution across 359 zones
  • Data Center Cooling. 50MW liquid-to-air cooling optimization with PUE tracking
  • Substation & Microgrid. 33/11kV transformer thermal modeling and phase balance

03Compliance

Twelve frameworks, mapped to controls

These are architectural readiness mappings, not certifications held by Ideaxa. Each row shows the evidence a client's auditor can trace in the delivered system.
Compliance frameworks with the architectural controls and evidence used to meet them
SOC 2 Type IIAICPA · Security & Cloud GovernanceMulti-account AWS Organizations & Azure vWAN isolation with automated SCP guardrails and quarterly penetration tests.
  • Zero-trust WireGuard mesh segmentation (NetBird) isolating production workloads
  • Immutable audit trails in ClickHouse with cryptographic timestamping
  • Role-based access control (RBAC) with MFA enforced across all landing zones
ISO/IEC 27001:2022International Organization for Standardization · Security & Cloud GovernanceDocumented ISMS architecture, automated Terraform state encryption, and multi-region backup pipelines.
  • Annex A controls: Information security policies, asset management, and access controls
  • Cryptographic key management with automated key rotation and HSM/KMS backends
  • Formal threat modeling (STRIDE) applied to all microservices and API gateways
HIPAA / HITECHU.S. Department of Health & Human Services · Data & PrivacyArchitected hybrid life-sciences instrumentation telemetry for TCS enterprise clients with zero unencrypted data pathways.
  • End-to-end AES-256 encryption at rest across all ZFS NVMe pools and S3 buckets
  • Mandatory TLS 1.3 in transit with strict mTLS between microservices
  • Business Associate Agreement (BAA) boundary isolation within dedicated VPCs
GDPR & India DPDP Act 2023European Commission & Government of India · Data & PrivacyPrivate on-premises LLM inference (LiteLLM/Ollama) eliminating cloud API data leakage and sovereign ClickHouse data storage.
  • Sovereign bare-metal data residency ensuring data never traverses unapproved jurisdictions
  • Automated PII scrubbing pipelines prior to analytical indexing or vector embedding
  • Cryptographic erasure primitives for deterministic user data deletion
NIST SP 800-53 Rev. 5NIST · Security & Cloud GovernanceBaseline control mapping implemented across all Terraform modular landing zones and Proxmox unprivileged LXC containers.
  • Access Control (AC) and Identification & Authentication (IA) via centralized IdP and WebAuthn
  • Audit and Accountability (AU) with centralized SIEM forwarding and tamper-proof storage
  • System and Communications Protection (SC) through mutual TLS and network micro-segmentation
PCI-DSS v4.0PCI Security Standards Council · Security & Cloud GovernanceArchitected fintech payment gateway infrastructure with zero-downtime database migration and automated tokenization.
  • Complete network isolation of payment tokens using dedicated subnet boundaries
  • Strict zero-trust ingress filtering via Cloudflare / Azure Front Door WAF
  • Mandatory MFA for all administrative access and bastion jump-hosts
CIS Benchmarks Level 1 & 2Center for Internet Security · Cloud & InfrastructureProxmox hypervisors and production Kubernetes clusters audited against CIS benchmarks with 98%+ compliance score.
  • Linux kernel hardening: disabled unnecessary file systems, restricted core dumps, tuned sysctl
  • Rootless container execution and unprivileged namespaces in LXC/Docker
  • Kubernetes CIS hardening: API server flags, NetworkPolicies, and Pod Security Standards (Restricted)
IEC 62443-4-2 / ISA-99International Electrotechnical Commission · Industrial & SCADAIndustrial telemetry networks and 9 digital twins operating across commercial chillers, VRF units, and electrical substations.
  • Purdue Model zoning: strict separation between Level 0/1 field sensors, Level 2/3 SCADA, and Level 4 enterprise IT
  • Air-gapped unidirectional gateways and Modbus/BACnet proxy isolating operational technology
  • Cryptographic device authentication for field LoRaWAN and Modbus RTU telemetry nodes
FedRAMP High / ModerateFedRAMP PMO · Cloud & InfrastructureLanding zone Terraform modules with FedRAMP High compliant parameter profiles and encryption policies.
  • FIPS 140-3 validated encryption algorithms enforced across all storage and transport layers
  • Dedicated GovCloud / isolated tenant architectures preventing noisy-neighbor risks
  • Continuous monitoring and automated boundary telemetry dispatch
ISO 9001:2015ISO · Operational QualityMaintained 100% on-time delivery across multi-year consulting engagements at Ideaxa Solutions.
  • Strict architectural review boards (ARB) for all production infrastructure modifications
  • Automated CI/CD validation gates: linting, unit testing, SAST, and integration benchmarks
  • 100% on-time project delivery track record through milestone tracking and sprint cadence
NIST CSF 2.0NIST · Security & Cloud GovernanceComprehensive cybersecurity posture implemented across bare-metal data-lake nodes, Proxmox hypervisors, and cloud VPCs.
  • Govern: Clear organizational risk tolerance policies and infrastructure ownership matrices
  • Identify & Protect: Complete asset discovery and zero-trust boundary segmentation
  • Detect: Real-time telemetry monitoring with sub-50ms ClickHouse anomaly queries
OWASP Top 10 & LLM Top 10OWASP Foundation · AI & Application SecurityLiteLLM sovereign proxy and FastMCP tool bus governing all agentic LLM executions with complete input/output sandboxing.
  • Prompt injection sanitization and adversarial intent classification at the API proxy layer
  • FastMCP (Model Context Protocol) sandboxed execution with strict JSON-RPC schema verification
  • Model denial-of-service prevention through strict token governance and request rate limiting

Want this kind of outcome on your platform?

Send a two-minute brief. You get a reply from me with a first view on approach, timeline and cost.