AWS & Azure Enterprise Landing Zones
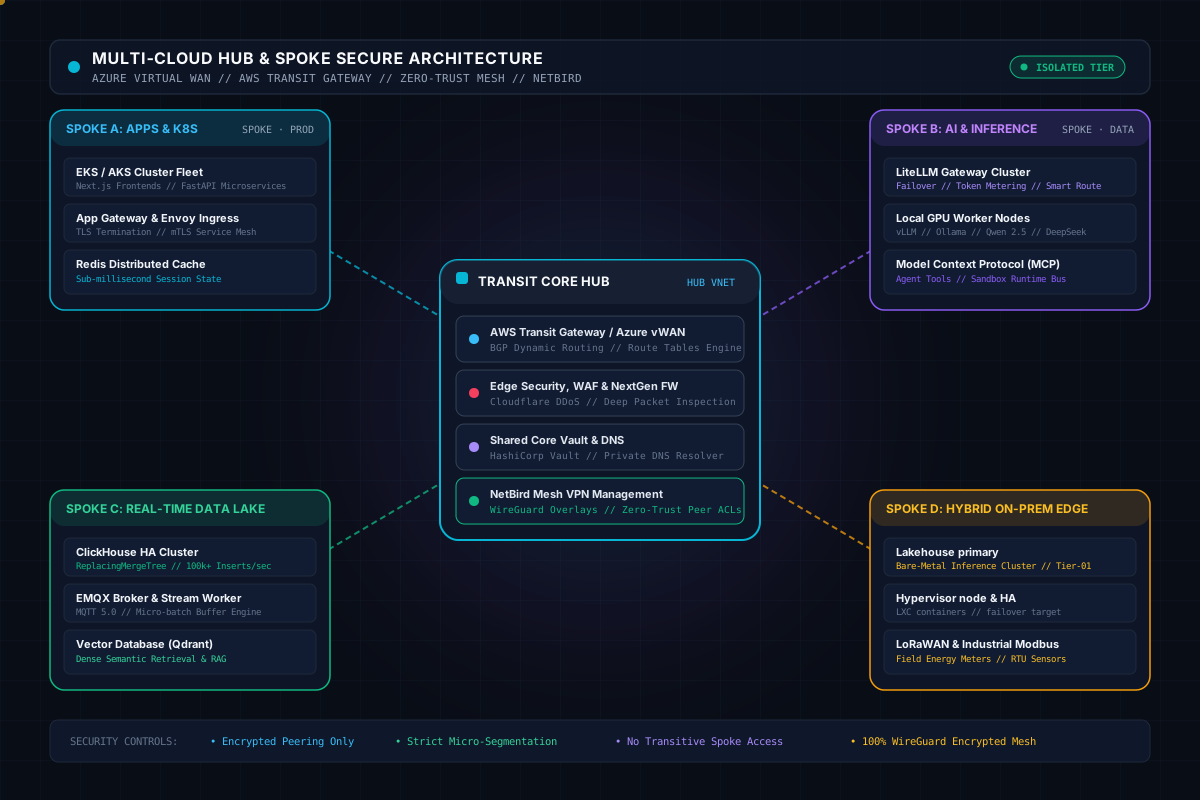
Production-grade multi-account architectures designed for security, governance, and seamless hybrid cloud interconnectivity.
Show detail (4)Hide detail
- Multi-Account Governance: AWS Organizations, AWS Control Tower, Service Control Policies (SCPs), and Azure Management Groups with strict subscription isolation.
- Hybrid Networking: AWS Transit Gateway, Azure Virtual WAN, Hub-and-Spoke VPC peering, and IPsec VPN / Direct Connect / ExpressRoute dedicated routing.
- Least-Privilege Security Boundaries: IAM permission boundaries, fine-grained role-based access control (RBAC), KMS/Key Vault envelope encryption, and AWS GuardDuty/Azure Defender security postures.
- Egress & Ingress Control: Centralized NAT Gateway inspection pools, Web Application Firewalls (AWS WAF, Azure Front Door), and GeoIP egress filters.